

Recently Posted
CredShields Blog
Latest articles
What Sony & Rockstar’s GTA 6 Launch Architecture Teaches Us About High Stakes Releases
Tonight at midnight, millions of consoles unlock Grand Theft Auto VI at the exact same moment. Players have...
You Hand an Agent Scope and Credentials. Then What?
Agentic pentesting works in stages once you provide scope and credentials: the agents map the application, identify attack...
The Flaws Your Scanner Will Never Flag, and Why Attackers Love Them
Business logic vulnerabilities let a user break the rules of an application using requests that are completely valid....
What Happens When Attacking Your Company Costs Almost Nothing?
AI cyberattacks are removing the economic cover small targets once had. Attacks used to cost hours of skilled...
Is AI-Generated Code Security Keeping Up With AI-Assisted Attackers?
AI coding tools give developers and attackers the same kind of speed, and the security gap comes from...
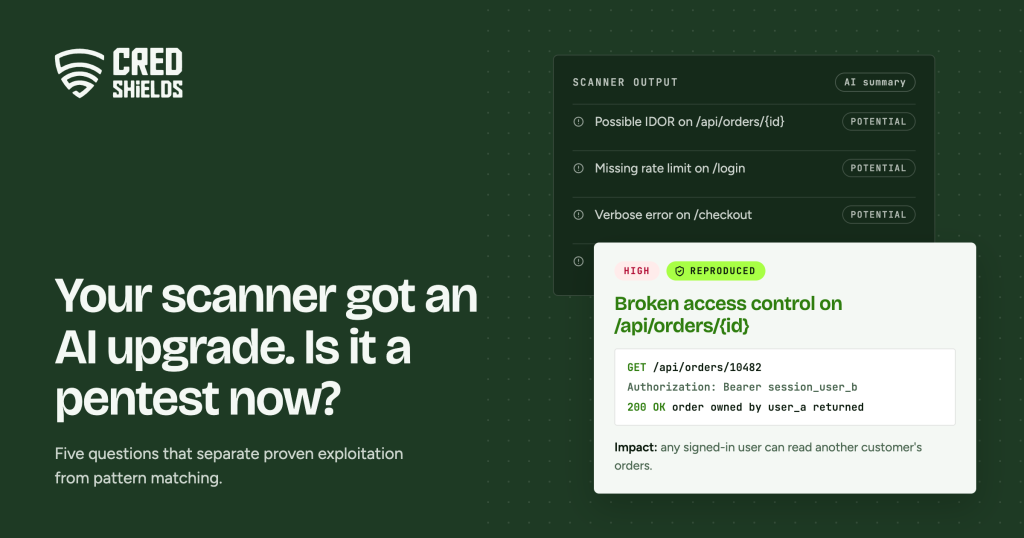
Your Scanner Got an AI Upgrade. Is It a Pentest Now?
AI pentesting means AI agents attack a running application, attempt exploitation, and report what they reproduce. A scanner...
The Hidden Cost of False Positives: How Scanner Noise Drains Engineering Velocity
Most security tools promise to protect your software before it reaches production. You turn them on, run a...
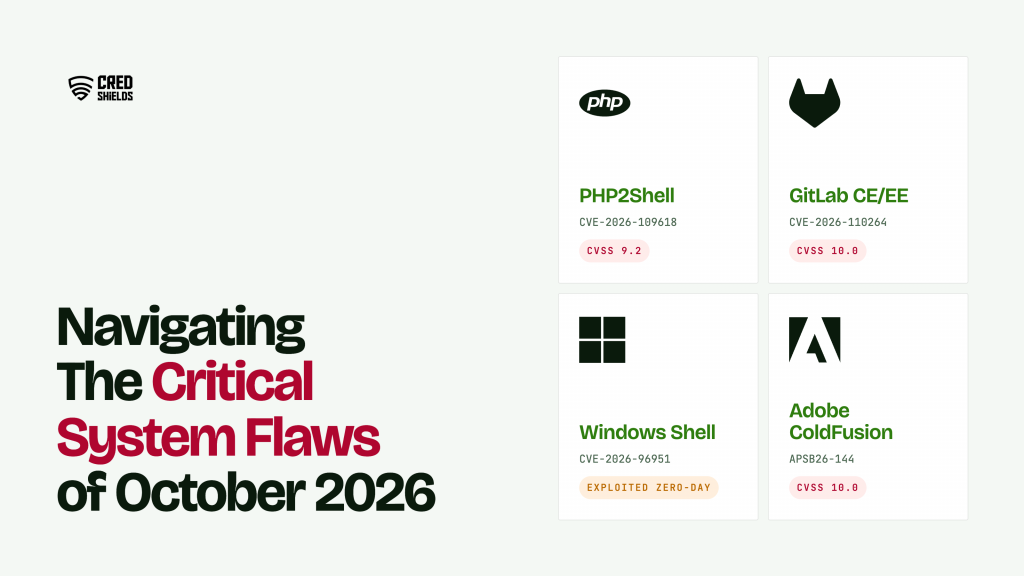
PHP2Shell RCE & GitLab CVSS 10 Exploit: How to Secure Backend Runtimes Against Critical Infrastructure Threats
Right now, global digital infrastructure is facing one of the most chaotic and dangerous periods we’ve seen in...
Why API Security Fails When You Only Test Syntax Instead of Behavior
Modern software runs on APIs. Every mobile app, web dashboard, and microservice talks to your backend through API...
5 Business Logic Flaws Automated Scanners Never Catch (And How Attackers Exploit Them)
Automated scanners are great at finding known code mistakes. They check syntax, flag outdated packages, and catch missing...